Website security monitoring can flag suspicious activity, but a flag is a reason to look closer, not proof that someone broke into your site. A scan can find indicators it was designed to check for. An alert can draw attention to a change or pattern. A person still needs to establish what happened, what it affected, and what action is appropriate.
Knowing the difference helps you respond calmly and avoid two costly mistakes: ignoring a real warning or treating every unusual event as a confirmed breach.
Three distinct jobs: scanning, alerting, and response
A scan checks for selected indicators
Website malware scanning compares files or site behavior against indicators its method can recognize. Depending on the scan, that may include known malicious code, suspicious file changes, or other signs associated with malware. An external check may see public-facing pages, while an application or server-level check may have access to different information.
No scan sees everything. Results depend on what it checks and what parts of the site it can access. A clean result means the scan did not find indicators within its scope; it does not prove that no unauthorized access occurred.
An alert asks for attention
Website security alerts can be triggered by events such as repeated failed logins, an unexpected administrator account, a changed file, or a redirect that was not expected. These are examples of signals a monitoring setup may be able to flag, not a promise that every system watches for each one.
Context matters. A legitimate site update can change files. A staff member or developer may have created an administrator account as part of approved work. A burst of failed logins can indicate attempted access without showing that anyone got in. The alert identifies something to check; it does not explain the whole story.
Incident response verifies and acts
Website incident response is the work of investigating a concern, determining its scope, and choosing next steps. That may involve reviewing account activity, server and application logs, file changes, and recent site updates. A responder may then need to contain access, remove malicious changes, secure affected accounts, or restore clean files.
Those are separate tasks from scanning and alerting. When you evaluate a monitoring service, ask who reviews alerts, what information they can inspect, how concerns are escalated, and whether investigation or cleanup is part of the service. Around-the-clock monitoring does not, by itself, tell you whether a person is reviewing each alert or how quickly remediation will happen.
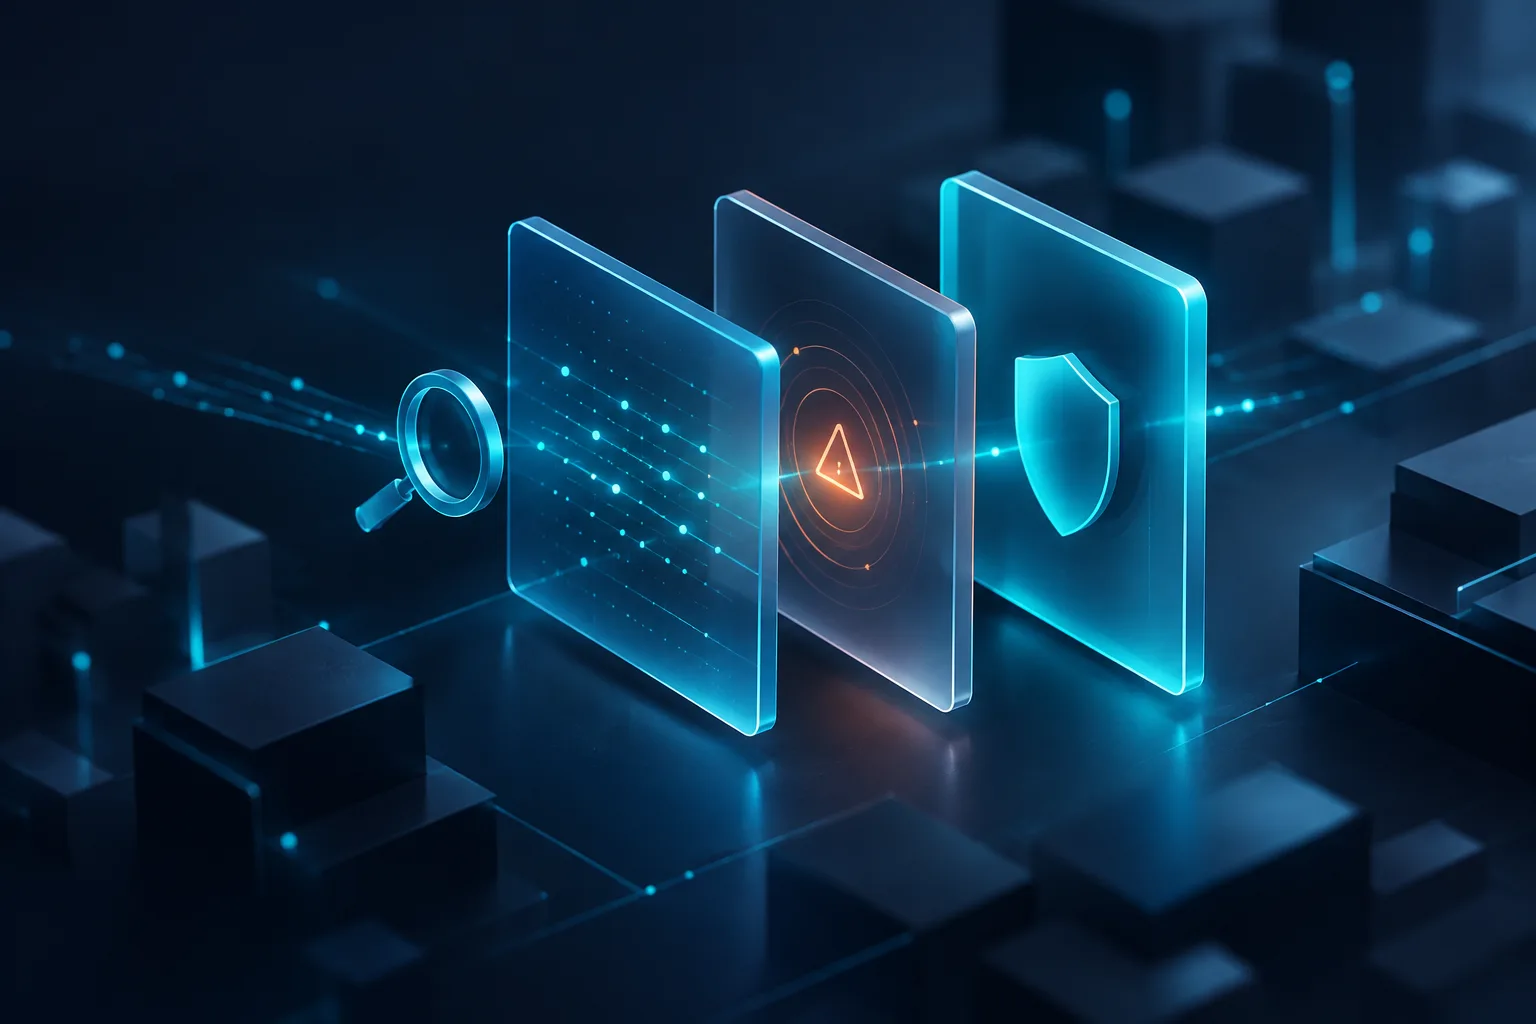
What monitoring may flag, and what a person should verify
- Repeated failed logins: Check whether the attempts targeted an account that exists and whether any login succeeded. Failed attempts alone do not establish access.
- An unfamiliar administrator account: Confirm with the people responsible for the site whether the account was authorized. If it was not, review when it appeared and what activity followed.
- Unexpected file changes: Compare the timing with recent updates or approved work. A file change can be expected or suspicious; the change itself needs context.
- Redirects or unfamiliar pages: Check whether the behavior is consistent across pages and visits, and whether a recent site change explains it. A redirect may warrant investigation even if a scan does not report malware.
- Unusual activity in logs: Look for related events around the same time, such as account changes or access to sensitive parts of the site. Logs can help build a timeline, but may be incomplete or not cover every system.
Logging guidance from OWASP’s Logging Cheat Sheet explains why useful logs should capture relevant events and enough context to support review. In practice, the available record depends on what the site and its hosting environment record and retain.
What to do when an alert looks suspicious
- Record what you saw. Note the alert, the affected page or account, and when you noticed it. Keep screenshots or copies of the message when useful.
- Contact your hosting or security provider. Share the alert and ask what the system detected, what it checked, and whether anyone has reviewed the event.
- Preserve relevant records. Avoid deleting files or clearing logs before the issue is assessed. Logs, timestamps, and recent change details may help establish what happened.
- Confirm recent authorized work. Check with staff or vendors who may have changed files, accounts, or site settings. This can help distinguish routine work from activity that needs a closer look.
- Follow a coordinated response. If there are signs of unauthorized access, have the responsible provider or qualified responder assess the scope and recommend containment and recovery steps. Avoid assuming that a clean scan resolves the concern.
The NIST guidance on incident response and cybersecurity risk management treats response as an organized process, not just a scan or alert. For a website owner, the practical takeaway is to preserve useful information, get the right people involved, and verify the situation before deciding what to change.
Ask what “monitoring” includes
Before relying on a monitoring description, ask whether it means automated checks only, alerts sent to you, human review, or hands-on investigation and remediation. Also ask what the checks cover, where alerts go, and what happens when the site owner or provider cannot immediately confirm whether activity is legitimate.
Zevonix provides security monitoring and malware scanning around the clock. Its hosting also includes managed updates and patching, and encrypted off-site backups that run nightly and are checked. These facts describe monitoring and care features; they do not mean every alert receives immediate human investigation or that monitoring prevents every attack. You can read more about website hosting security and website care.
Frequently asked questions
Can a website security scan confirm that my site was hacked?
A scan can find indicators within its scope, but it cannot always confirm whether unauthorized access occurred. A person may need to review accounts, logs, file changes, and site behavior.
What should I do when I receive a suspicious website security alert?
Record what the alert says and when you received it, preserve relevant records, and contact your hosting or security provider. Ask what was detected and what should be checked before making changes.
Does around-the-clock monitoring mean someone will fix an attack immediately?
Not necessarily. Monitoring may refer to automated checks, alerts, or human review. Ask the provider who reviews alerts and whether investigation and remediation are included.
What evidence should I preserve if I suspect a compromise?
Keep the alert, relevant timestamps, screenshots, account and file-change details, and available logs. Avoid deleting records before a provider or responder has a chance to assess them.
Take the next step
Monitoring is most useful when you know what it checks and what happens after an alert. If you want to discuss managed hosting and website care, get in touch with Zevonix.